Render Alternatives in 2026
The best Render alternatives in 2026 for teams that want a managed workflow with more control over their backend infrastructure.
Render covers web services, workers, scheduled jobs, and Postgres with a managed deployment workflow. As companies grow, engineering teams often want to run the backend in their own AWS or GCP account, with more control over networking, scaling, and access to other cloud services. Developers and agents still need to add features and test changes across the backend without taking on all the infrastructure setup that Render handles today.
For teams looking for Render alternatives, the problems tend to include:
- A new API or worker depends on cloud resources outside the services configured in Render.
- Production needs to run within the networking, IAM, and infrastructure policies of an existing AWS or GCP account.
- Developers maintain local dependencies separately from the services and databases described in the deployment Blueprint.
- Costs need to be planned across service instances, databases, storage, and transfer as the backend grows.
- Agents update application code and deployment configuration, and the team needs to verify resource connections and permissions together.
Render alternatives at a glance
| Alternative | Approach | Best fit |
|---|---|---|
| Encore | Type-safe APIs and infrastructure in application code, deployed to your AWS or GCP account | Teams that want developers and agents to work with backend resources while platform teams control production |
| Railway | Repository or container deployment with connected services and isolated environments | Teams deploying an existing stack with connected services |
| Fly.io | Container workloads on regionally placed Machines | Teams that need regional placement and Machine control |
| Coolify | Self-hosted deployment tooling for repositories, containers, and Compose | Teams prepared to operate their own servers and deployment platform |
| DigitalOcean App Platform | Managed services, workers, and jobs within DigitalOcean | Teams already using DigitalOcean infrastructure |
Encore: backend code with infrastructure under your control
Encore combines the simplicity of a managed backend platform with infrastructure in your own AWS or GCP account, defined through type-safe primitives in application code. Developers and agents work with services, APIs, databases, Pub/Sub, buckets, caches, cron jobs, and secrets, while platform teams control how those resources run. The application runs on standard cloud services and can be built as a Docker image for deployment outside the Encore platform.
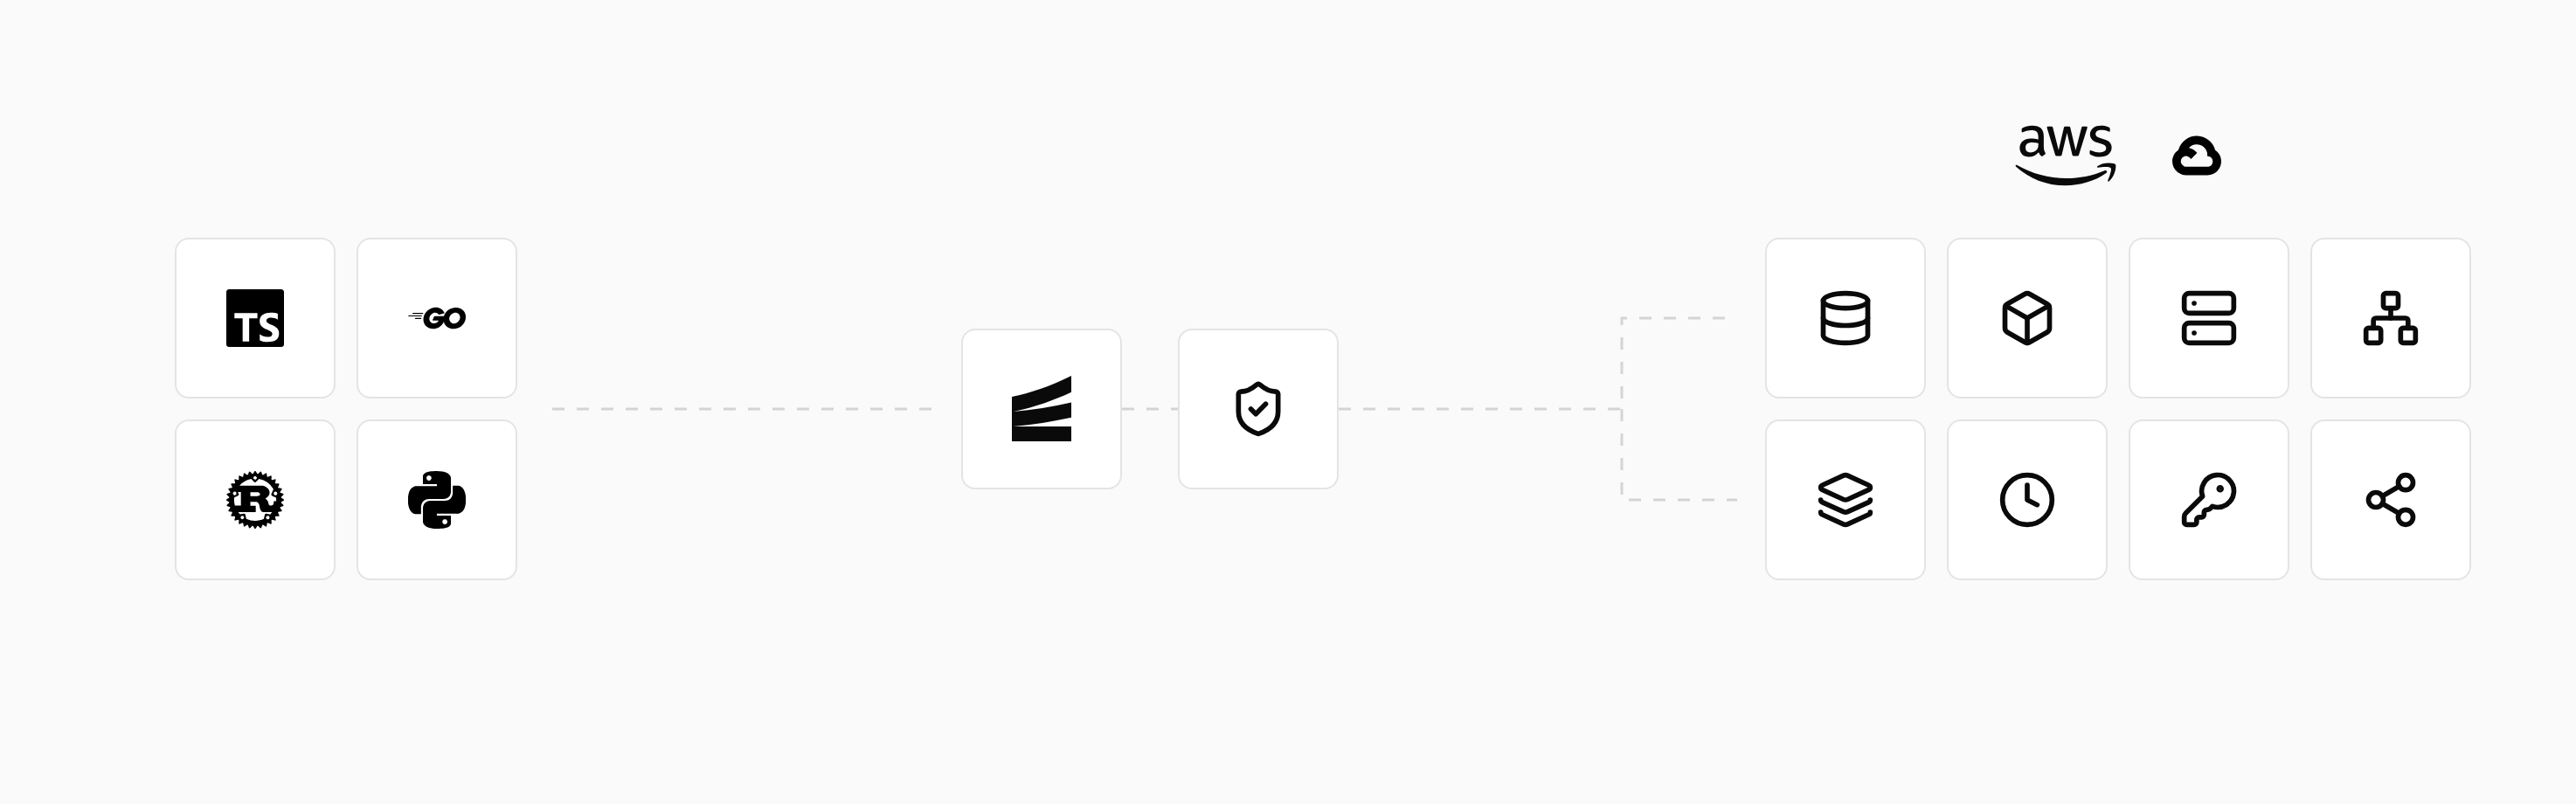
Encore uses static analysis to read the API and resource declarations without running the code, building an application model of service dependencies, resource connections, and the IAM needed for supported resources.
For services moving from Render into your AWS or GCP account, developers define APIs and resource dependencies in application code, while platform teams control sizing, scaling, networking, and regions through environment configuration. Encore provisions supported resources with integrated logs, metrics, and tracing. Existing Terraform can continue managing shared or unsupported infrastructure.
Working with agents

encore run. The same bucket declaration is used in preview environments and production.A database, bucket, Pub/Sub topic, or any other supported infrastructure resource is declared in the code that uses it. When an agent adds one:
- APIs, business logic, and resource dependencies can be reviewed in the same pull request, with generated clients providing typed access from the frontend.
- From the first
encore run, the agent can test the change against local infrastructure, then check it end to end in an isolated preview environment on Encore Cloud, or in your own cloud account on Enterprise. - The same application definitions drive local development, previews, and production, keeping services and resource dependencies consistent while capacity and cloud settings are configured per environment.
- The agent can use type errors, traces, and logs to find and fix failures, and test the authorization checks and business rules in the API before opening a pull request.
- Platform teams can configure separate processes per service for independent deployment and scaling, with Pub/Sub subscribers for asynchronous work and cron jobs for scheduled processing.
- Platform teams keep control of production configuration and credentials through their access controls, while developers work with application-level resources.
Cloud resources are billed directly in your account, with costs determined by the services and capacity your team configures, alongside Encore's platform fee.
Best for
Encore fits engineering teams that like Render's managed workflow but need production in their own AWS or GCP account, with application resources defined and tested alongside the code that uses them.
Adoption can start with one API while Render keeps hosting the existing application. Reachable services and databases can remain external dependencies during migration. Background workers need to be mapped by their trigger and lifecycle: Pub/Sub handles event consumers and cron handles scheduled operations; persistent disks and arbitrary long-running processes need a separate design or can stay on Render.
See the migration guide for workload mapping and adoption steps.
Railway: connected services with a flexible deployment workflow
Railway deploys applications from repositories or container images, with database templates, volumes, cron jobs, and private networking. Reference variables connect services to each other's addresses and credentials, while deployment settings can live in TOML or JSON.
Working with agents
Railway provides MCP and agent tooling for inspecting and managing deployments. Agents can work with the existing application framework, configure services, and test changes in isolated PR environments. Resource connections use Railway configuration and reference variables, alongside the dependencies expressed in application code.
Best for
Railway fits teams that want to deploy an existing backend and its dependencies without adopting a new framework. Its standard offering runs on Railway infrastructure, with usage billing and spending controls. Railway also advertises Enterprise BYOC for deployment in an existing VPC; teams that only need a different hosting location should evaluate that option before migrating the application.
Fly.io: containers deployed close to your users
Fly.io runs container images on Machines in regions you select. Fly Launch handles common deployment tasks, while Machine configuration gives teams control over processes, compute, and lifecycle behavior. It suits workloads where placing compute near users matters.
Working with agents
Agents can edit the Dockerfile and fly.toml, deploy through flyctl, and use the Fly MCP server to operate apps. Testing a change includes the application and its Machine configuration, network paths, and storage behavior. Volumes are local to a server, with replication handled by the application or another storage system.
Best for
Fly.io fits teams that need regional placement and direct control over container workloads on Fly's infrastructure. Check the operational requirements of each workload: Fly's managed Postgres and an application using local volumes have different backup, replication, and failover responsibilities.
Coolify: a deployment platform on servers you control
Coolify provides a deployment dashboard for applications, databases, and services on your own servers. It supports repository builds, container images, and Docker Compose, so an existing backend can keep its framework and deployment packaging.
Working with agents
Agents can edit the application, Dockerfile, or Compose configuration and trigger deployments through Coolify's API or repository integration. Preview deployments run pull requests separately from production. Your team configures the resources and credentials each application uses, including how previews connect to databases and other stateful services.
Best for
Coolify fits teams that want a PaaS-like dashboard on their own VPS or cloud servers and have the capacity to operate it. Server security, platform updates, backups, recovery, and capacity planning remain part of the team's work. Self-hosting changes who controls the deployment without requiring the backend to adopt a new application model.
DigitalOcean App Platform: managed hosting within DigitalOcean
DigitalOcean App Platform builds and deploys web services, static sites, workers, and jobs. Applications can connect to DigitalOcean Managed Databases and other services in the same ecosystem.
Working with agents
An agent can edit the application's app spec and deploy it through the API or doctl. The spec describes components, instance settings, environment variables, and database connections. Local testing uses the application's existing framework and tooling, with cloud configuration checked separately.
Best for
App Platform fits teams already using DigitalOcean that want managed application hosting alongside its databases and storage. It keeps the backend on DigitalOcean rather than deploying into an existing AWS or GCP account. Compare component sizes, scaling behavior, database costs, and transfer charges against your workload.
How to choose
Choose Railway for a flexible service-and-template workflow, Fly.io for regional placement and Machine control, or DigitalOcean App Platform if the backend already uses DigitalOcean. Coolify fits teams prepared to operate their own deployment platform. Encore fits teams that need production in their own AWS or GCP account and want resource definitions, local testing, and application changes in the same development workflow.
Frequently asked questions
What is the best alternative to Render?
Encore for application-defined infrastructure in your own AWS or GCP account, Railway for flexible service deployment, Fly.io for regional container placement, Coolify for self-hosting, or DigitalOcean App Platform for managed hosting in DigitalOcean.
Does Render support private networking and preview environments?
Yes. Render has private networking between services in the same region, and Blueprint-based preview environments can reproduce groups of services and databases for pull requests.
Can I migrate a Render worker to Encore?
Event-driven work can use Encore Pub/Sub subscribers, and scheduled work can use cron jobs. Arbitrary long-running processes and disk-dependent workers are not direct equivalents; retain them as external services or redesign them for the target runtime.
Do Encore environments use identical infrastructure locally and in production?
No. The same application definitions describe services and resource dependencies across local development, previews, and production. Local implementations and cloud capacity differ by environment. Preview environments run on Encore Cloud by default; own-account previews are available on Enterprise.
Is Encore a drop-in host for an existing container?
No. Backend operations use Encore APIs and supported resource declarations. You can adopt it incrementally, but migrating is a development-model change rather than moving an unchanged container image.
Does using my own cloud account make costs fixed?
No. AWS or GCP charges depend on the resources, capacity, and usage your team configures, alongside Encore fees. Cloud ownership gives you native billing visibility and configuration control, not a guarantee of lower or fixed costs.
Ship without waiting on Terraform
Encore lets developers and agents define application infrastructure directly in code, then automatically provisions it from local development to production in your AWS or GCP account.