How to Add Secrets to a Go API
API keys and webhook signing secrets in a Go service, with Encore or AWS Secrets Manager, on AWS and locally.

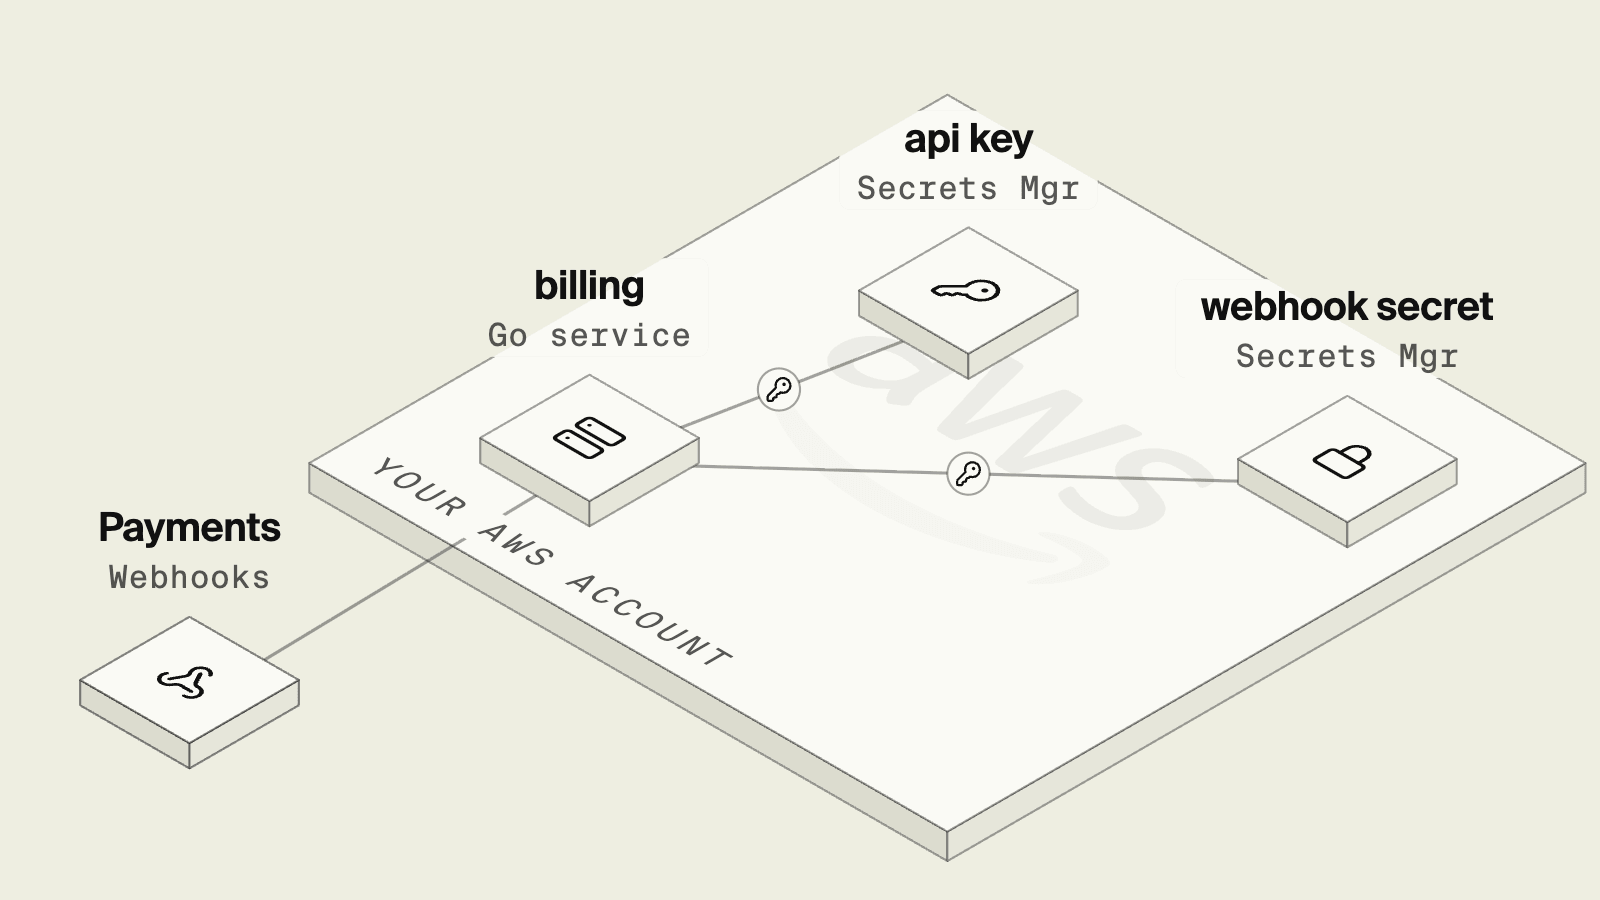
The most direct way to manage secrets for a Go API on AWS and locally is Encore: you declare the keys as fields on a secrets struct in the service, set values with encore secret set, and on deploy to your own AWS or GCP account those values are copied into AWS Secrets Manager or GCP Secret Manager. Encore provisions an IAM role for the service, or a service account on GCP, so the process does not need long-lived AWS access keys. The hand-built path is AWS Secrets Manager plus the AWS SDK for Go v2 or ECS task injection, a common pattern for Go services on Fargate.
This guide adds two secrets to a Go service that receives payment webhooks: an API key for outgoing calls and a signing secret that verifies incoming webhooks. Code samples use encore.dev 1.58.9 and the AWS SDK for Go v2 (release 2026-11-16).
What are the options for secrets in a Go API?
The verdict: pick Encore when you want the declaration, the local value, and the production secret in one workflow, and Encore provisions an IAM role for the service, or a service account on GCP. Pick Secrets Manager with ECS injection when the task definition is already the source of truth.
How do you declare secrets in Encore?
Encore is a backend framework for Go with built-in infrastructure, and its platform deploys into your own AWS or GCP account. Secrets are fields on a package-level struct named secrets, and Encore fills them in before the service handles its first request. The webhook is a raw endpoint so the signature is checked against the exact bytes that arrived:
// Service billing receives payment webhooks. (encore.dev 1.58.9)
package billing

import (
	"crypto/hmac"
	"crypto/sha256"
	"encoding/hex"
	"io"
	"net/http"

	"encore.dev/rlog"
)

// Encore loads these values at startup. Set them with `encore secret set`.
var secrets struct {
	PaymentsAPIKey        string // used for outgoing calls to the payments API
	PaymentsWebhookSecret string // verifies incoming webhook signatures
}

// Webhook checks the HMAC signature before trusting the payload.
//
//encore:api public raw method=POST path=/webhooks/payments
func Webhook(w http.ResponseWriter, req *http.Request) {
	body, err := io.ReadAll(http.MaxBytesReader(w, req.Body, 1<<20))
	if err != nil {
		http.Error(w, "body too large", http.StatusRequestEntityTooLarge)
		return
	}
	mac := hmac.New(sha256.New, []byte(secrets.PaymentsWebhookSecret))
	mac.Write(body)
	want := hex.EncodeToString(mac.Sum(nil))
	if !hmac.Equal([]byte(want), []byte(req.Header.Get("X-Signature"))) {
		http.Error(w, "invalid signature", http.StatusUnauthorized)
		return
	}
	rlog.Info("payment webhook verified", "bytes", len(body))
	w.WriteHeader(http.StatusNoContent)
}

// authHeader builds the header for outgoing calls to the payments API.
func authHeader() string {
	return "Bearer " + secrets.PaymentsAPIKey
}
For local development, the values can live in a .secrets.local.cue file at the app root, which you keep out of git, or be set with encore secret set --type local:
PaymentsAPIKey: "sk_test_local"
PaymentsWebhookSecret: "whsec_local"
Run the service and send a signed and an unsigned request:
In deployed environments the values are stored in the Encore secrets manager and, on deploy to your own cloud account, copied into AWS Secrets Manager or GCP Secret Manager. Encore provisions an IAM role for the service, or a service account on GCP. Production, development, and preview environments can each have their own values. If you set a production value separately from local or development, a test key does not have to reach production. Locally, a secret without a value is left empty and encore run prints a warning, and a deploy to an environment where a declared secret is missing reports which keys are not defined.
Secret values are not stored in the repository or in a .env file. An AI coding agent working in the codebase sees which secrets a service declares but does not see the values in the files it works with, and encore secret list only shows which environments have a value. The exception is a .secrets.local.cue override, a plaintext file in the app root, so keep it out of anything an agent should not read.
When an agent adds an integration, the new secret is a field in the struct it is already editing, and a missing value shows up as a warning under encore run before the change reaches production.
Run in your terminal to get started locally.
How do you use AWS Secrets Manager without Encore?
Without Encore, store the values in AWS Secrets Manager and give the task an IAM role that can read only those secrets. Do not put AWS access keys in the application.
How do you inject secrets through an ECS task definition?
The service can still read os.Getenv, and fail fast at startup when a value is missing:
type Config struct {
	PaymentsAPIKey        string
	PaymentsWebhookSecret string
}

func loadConfig() (Config, error) {
	c := Config{
		PaymentsAPIKey:        os.Getenv("PAYMENTS_API_KEY"),
		PaymentsWebhookSecret: os.Getenv("PAYMENTS_WEBHOOK_SECRET"),
	}
	if c.PaymentsAPIKey == "" || c.PaymentsWebhookSecret == "" {
		return c, errors.New("missing payments secrets")
	}
	return c, nil
}
Locally the values come from a .env file loaded by a library such as godotenv. In production on ECS, each secret is created in Secrets Manager and referenced from the task definition, and ECS injects it as an environment variable when the task starts:
The task execution role needs secretsmanager:GetSecretValue on both ARNs. Values are read when the task starts, so rotating a secret means starting new tasks. Staging needs its own set of secrets and its own task definition pointing at them.
A .env file sits in the project directory, where any AI coding agent or tool with access to the repository can read it, and that is a common way keys end up in prompts, logs, or commits.
How do you fetch a secret with the AWS SDK for Go v2?
If you would rather load the secret in process, use the AWS SDK for Go v2 and read it at startup. Cache the value rather than calling Secrets Manager on every request. The task role, not an access key in the environment, should be what authenticates the client:
package secretsloader

import (
	"context"
	"encoding/json"
	"fmt"

	"github.com/aws/aws-sdk-go-v2/config"
	"github.com/aws/aws-sdk-go-v2/service/secretsmanager"
)

type paymentsSecrets struct {
	APIKey        string `json:"api_key"`
	WebhookSecret string `json:"webhook_secret"`
}

func loadPayments(ctx context.Context, secretID string) (paymentsSecrets, error) {
	cfg, err := config.LoadDefaultConfig(ctx)
	if err != nil {
		return paymentsSecrets{}, err
	}
	out, err := secretsmanager.NewFromConfig(cfg).GetSecretValue(ctx, &secretsmanager.GetSecretValueInput{
		SecretId: &secretID,
	})
	if err != nil {
		return paymentsSecrets{}, err
	}
	if out.SecretString == nil {
		return paymentsSecrets{}, fmt.Errorf("secret %s has no string value", secretID)
	}
	var s paymentsSecrets
	if err := json.Unmarshal([]byte(*out.SecretString), &s); err != nil {
		return paymentsSecrets{}, err
	}
	if s.APIKey == "" || s.WebhookSecret == "" {
		return paymentsSecrets{}, fmt.Errorf("secret %s is missing keys", secretID)
	}
	return s, nil
}
Enable rotation in Secrets Manager where it is appropriate, and make sure a new task or a refresh path can pick up the new value. SSM Parameter Store is the lighter alternative for values that do not need rotation; the injection path is the same shape, with ssm:GetParameters on the execution role instead of secretsmanager:GetSecretValue. For a SecureString encrypted with a customer-managed KMS key, the execution role also needs kms:Decrypt on that key, and the key policy must permit the role.
How should you choose?
Pick Encore when you want secrets declared as part of the Go service, with local values for each developer and separate production values stored in your own AWS or GCP account. The same service can use a Postgres database whose credentials Encore manages for you.
Pick environment variables with Secrets Manager, or a GetSecretValue call at startup, when your ECS task definitions are already managed in Terraform and the team is used to that flow.
Related guides
- How to manage secrets on AWS with an AI agent
- The best secrets management tools
- How to Add Secrets to an Axum App
- How to Add Secrets to a FastAPI App
- How to Add Secrets to a Go net/http App
- What Is AWS Secrets Manager? Rotation, IAM and App Access
- How to Use AWS Secrets Manager With ECS Fargate
- How to Manage Secrets in a Gin App
Frequently asked questions
How do I manage secrets for a Go API on AWS and locally?
With Encore, declare var secrets struct { PaymentsAPIKey string } in the service package and set the value with encore secret set --type production PaymentsAPIKey. Encore loads the value at startup locally and in each environment, and when you deploy to your own AWS or GCP account it is copied into AWS Secrets Manager or GCP Secret Manager. Without Encore, store the values in AWS Secrets Manager, inject them through the ECS task definition or fetch them at startup with the AWS SDK for Go v2, and give the task an IAM role rather than putting access keys in the app.
Where should a Go service read secrets from on AWS?
Store them in AWS Secrets Manager or SSM Parameter Store and inject them as environment variables through the ECS task definition, or fetch them at startup with the AWS SDK. Avoid baking them into the image or committing them in a .env file.
How do I compare webhook signatures safely in Go?
Compute the HMAC of the raw request body with crypto/hmac and compare with hmac.Equal, which runs in constant time. Read the body once with a size limit before parsing it as JSON.
Deploy to your cloud on AWS and Google Cloud
without managing infrastructure
Encore lets developers and agents define application infrastructure directly in code, then automatically provisions it from local development to production in your AWS or GCP account.
